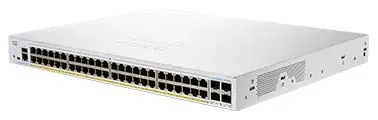
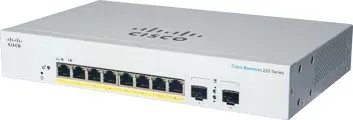
Cisco switch CBS250-16T-2G (16xGbE,2xSFP,fanless)
Cena včetně DPH
Cena zahrnuje recyklační příspěvek 2 Kč
Zboží je skladem u našeho dodavatele — odesíláme ho, jakmile ho od něj převezmeme.
U vás:
- Výrobce
- Cisco
- Model
- CBS250-16T-2G-EU-RF
- Kód
- IDE-1608013
Použité zboží
- Stav
- BStav B — známky používání
- Poznámky ke stavu
- Repasováno výrobcem (Cisco Refresh)
- Záruka
- 12 měsíců
Popis
Cisco switch CBS250-16T-2G - REFRESH
CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu
Řada Cisco Business 250 představuje novou generaci cenově dostupných inteligentních switchů, které kombinují vysoký síťový výkon, zabezpečení a spolehlivost s komplexní sadou síťových funkcí potřebných pro spolehlivou síť malých firem.
Záruka platná do End of Support 31. 10. 2029.
Oznámení End of Life pro CISCO CBS250
Stránky produktu: CBS250-16T-2G
Quick start guide: Quick start guide
Switching capacity (All switches are wire-speed and nonblocking)
Forwarding rate in millions of packets per second (mpps; 64-byte packets) 26,78
Switching capacity in Gigabits per second (Gbps) 36
Layer 2 switching
Spanning Tree Protocol (STP) Standard 802.1d spanning tree support
Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default
Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported
Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported
Rapid PVST+ (RPVST+); 126 instances are supported
Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP)
Up to 4 groups
Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG)
VLAN Support for up to 255 active VLANs simultaneously
Port-based and 802.1Q tag-based VLANs
Management VLAN
Guest VLAN
Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices
Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Protocols for automatically propagating and configuring VLANs in a bridged domain
IGMP (versions 1, 2, and 3) snooping Internet Group Management Protocol (IGMP) limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported)
IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router
HOL blocking Head-of-Line (HOL) blocking prevention
Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP.
Layer 3 routing
IPv4 routing Wire-speed routing of IPv4 packets
Up to 32 static routes and up to 16 IP interfaces
IPv6 routing Wire-speed routing of IPv6 packets
Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface
Classless Interdomain Routing (CIDR) Support for CIDR
Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains
User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets
Security
Secure Sockets Layer (SSL) SSL encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch
Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported.
IEEE 802.1X (authenticator role) Remote Authentication Dial-In User Service (RADIUS) authentication, guest VLAN, single/multiple host mode, and single/multiple sessions
STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops)
Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received
Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices, and secure autoconfig. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user
Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products
Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC])
Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses
RADIUS Supports RADIUS authentication for management access. Switch functions as a client.
Storm control Broadcast, multicast, and unknown unicast
DoS prevention Denial-of-Service (DoS) attack prevention
Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels
Access Control Lists (ACLs) Support for up to 512 rules
Drop or rate limit based on source and destination MAC, VLAN ID or IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides
Time-based ACLs supported
QoS
Priority levels 8 hardware queues
Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and class of service (802.1p/CoS)
Class of service Port based; 802.1p VLAN priority based; IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based; Differentiated Services (DiffServ); classification and re-marking ACLs, trusted QoS
Rate limiting Ingress policer; egress shaping and rate control; per VLAN, per port, and flow based
Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization
Standards
Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flo…
Recenze
Tento produkt zatím nemá žádné recenze.
Recenze mohou psát pouze zákazníci, kteří produkt u nás koupili (na vyzvání po doručení objednávky). Všechny zveřejněné recenze proto pocházejí z ověřených nákupů.
Hodí se k tomu
Příslušenství a doplňky, které se k němu hodí
Podobné produkty
Ve stejné kategorii.