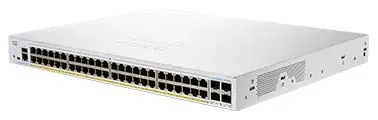
Cisco Catalyst switch C1300-48FP-4G (48xGbE,4xSFP,48xPoE+,740W)
Cena včetně DPH
Cena zahrnuje recyklační příspěvek 2 Kč
Zboží je skladem u našeho dodavatele — odesíláme ho, jakmile ho od něj převezmeme.
U vás:
- Výrobce
- Cisco
- Model
- C1300-48FP-4G-RF
- Kód
- IDE-1608381
Použité zboží
- Stav
- BStav B — známky používání
- Poznámky ke stavu
- Repasováno výrobcem (Cisco Refresh)
- Záruka
- 12 měsíců
Popis
Cisco Catalyst switch C1300-48FP-4G - REFRESH
CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu
Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu.
Stránky produktu: C1300-48FP-4G
Performance
Switching capacity and forwarding rate (All switches are wire-speed and nonblocking)
Capacity in millions of packets per second (mpps) (64-byte packets) 77.38
Switching capacity in gigabits per second (Gbps) 104.0
Layer 2 switching
Spanning Tree Protocol (STP) Standard 802.1d spanning tree support
Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default
Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported
Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported
Rapid PVST+ (RPVST+); 126 instances are supported
Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP)
Up to 8 groups
Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation
VLAN Support for up to 4093 VLANs simultaneously
Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN
Management VLAN
Private VLAN with promiscuous, isolated, and community port
Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN
Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN
Auto surveillance VLAN (ASV)
Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices
Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR)
VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN
Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers
Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs
Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag
Layer 2 protocol tunneling over Q-in-Q is also supported
Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain
Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect
Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks
DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82
Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported)
IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router
IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols
Head-of-Line (HOL) blocking HOL blocking prevention
Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP
Layer 3
IPv4 routing Wire-speed routing of IPv4 packets
Up to 990 static routes and up to 128 IP interfaces
IPv6 routing Wire-speed routing of IPv6 packets
Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface
Classless Interdomain Routing (CIDR) Support for CIDR
Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing
Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL)
DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes
Support for DHCP options
DHCP relay at Layer 3 Relay of DHCP traffic across IP domains
User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets
Security
Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported
Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch
IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and s…
Parametry
- Výkon
- 740 W
Recenze
Tento produkt zatím nemá žádné recenze.
Recenze mohou psát pouze zákazníci, kteří produkt u nás koupili (na vyzvání po doručení objednávky). Všechny zveřejněné recenze proto pocházejí z ověřených nákupů.
Hodí se k tomu
Příslušenství a doplňky, které se k němu hodí
Podobné produkty
Ve stejné kategorii.